Is vpn safe for gsa navigating security for federal employees and beyond
Is vpn safe for gsa navigating security for federal employees and beyond: A complete guide to VPN safety, compliance, and best practices
Is vpn safe for gsa navigating security for federal employees and beyond? In short: yes, but only if you choose the right VPN, configure it correctly, and follow federal and organizational guidelines. This guide breaks down everything you need to know so you can stay secure, private, and compliant while using a VPN in sensitive environments.
Is vpn safe for gsa navigating security for federal employees and beyond? Yes, with the right setup and policies, a VPN can significantly improve security for government workers, contractors, and anyone who needs to protect sensitive data on potentially risky networks. Here’s a quick overview of what you’ll learn: Unlock a truly private internet on your iphone ipad with nordvpn obfuscated servers
- How VPNs work in federal contexts, including encryption, authentication, and access control
- Key factors to evaluate for safety and compliance logs, NSA/DoD considerations, endpoint hygiene
- Step-by-step setup and best practices for safer remote work
- Common pitfalls and misconfigurations to avoid
- Real-world scenarios and quick-check checklists
Useful URLs and Resources plain text, not clickable Apple Website - apple.com, National Institute of Standards and Technology - nist.gov, National Security Agency - nsa.gov, Federal Information Security Management Act - fisma.gov, Cybersecurity and Infrastructure Security Agency - cisa.gov, Cloud Security Alliance - cloudsecurityalliance.org, VPN Security Guide - vpnsecurityguide.org, Privacy International - privacyinternational.org, ENISA - enisa.europa.eu, 2024 VPN Trends - 2024vpntrends.org
Who this guide is for
- Federal employees and contractors who must protect sensitive data
- IT and security professionals implementing or auditing VPN services
- Managers and decision-makers evaluating VPN vendors for compliance
- Anyone curious about how to navigate the balance between accessibility and security
What counts as a VPN in federal workflows
- A VPN Virtual Private Network creates an encrypted tunnel between your device and a trusted network, masking your traffic from eavesdroppers.
- In federal contexts, VPNs often support strong authentication multi-factor, strict access controls, split-tunnel vs. full-tunnel configurations, and centralized logging for audits.
- Common use cases: remote work for sensitive applications, secure access to internal portals, protecting data in transit on untrusted networks, and complying with data-handling requirements.
Key safety factors to evaluate data-driven and practical
- Encryption strength: Look for AES-256 or equivalent, robust key exchange IKEv2/IPsec, OpenVPN with strong ciphers, WireGuard with modern crypto.
- Authentication: Prefer multi-factor authentication MFA, certificate-based or hardware tokens, and strict session management.
- Logging and privacy: Federal guidance often requires minimization of unnecessary data and clear retention policies. Ensure vendor offers configurable logs, secure storage, and access controls.
- Endpoint security: A VPN is only as safe as the device on the other end. Enforce updated OS, antivirus, disk encryption, and regular software patching.
- Jurisdiction and data location: Understand where VPN providers store data and which laws apply. For federal use, be wary of jurisdictions that could compel data disclosure.
- Vendor transparency: Look for independent security audits, transparent disclosure policies, and evidence of compensating controls.
- Compliance alignment: Ensure the VPN supports DoD/DoN guidelines, FISMA compliance, and aligns with NIST SP 800-53 or equivalent controls.
Choosing the right VPN for federal and sensitive use The Top VPNs to Stream Einthusan Like a Pro Even When It's Blocked
- Enterprise-grade VPNs with strong security posture and admin controls
- Features to prioritize:
- Strong encryption and authenticated tunneling
- MFA support and certificate-based access
- Centralized policy management and role-based access control RBAC
- Detailed audit logs with controlled access for compliance reviews
- Endpoint posture assessment before granting access
- Support for split-tunneling only where appropriate, with strict controls
- Compatibility with DoD networks and government-grade hardware
- Vendor evaluation checklist:
- Security certifications and independent audits
- Data handling and retention policies
- Incident response and breach notification procedures
- Availability, SLAs, and disaster recovery plans
- Compatibility with government identity providers e.g., PIV, CAC, Federal Identity, Credential, and Access Management
- Clear guidance on remote access for mobile and desktop devices
Step-by-step setup and configuration guide
- Assess requirements
- Define which resources require VPN access, user roles, and acceptable risk levels
- Decide on full-tunnel vs split-tunnel: full-tunnel is typically safer for sensitive data
- Prepare identity and access controls
- Enforce MFA for all users
- Use certificate-based or hardware-token authentication when possible
- Implement RBAC to ensure users access only what they need
- Harden devices and networks
- Require up-to-date OS, security patches, and endpoint protection
- Enable disk encryption on endpoints
- Configure device posture checks before VPN connection is granted
- Configure the VPN server and policy
- Use strong encryption AES-256, secure key exchange, and modern protocols IPsec/IKEv2 or WireGuard
- Disable weak ciphers and keep software up to date
- Create clear access policies with time-bound sessions and automatic re-authentication
- Logging, monitoring, and incident response
- Capture only necessary data for audits and incident investigations
- Implement real-time monitoring for unusual login patterns or geolocation anomalies
- Define a clear incident response workflow and notification plan
- Testing and validation
- Run security tests, including vulnerability scans and penetration tests
- Validate MFA and device posture checks in real-world scenarios
- Ensure compliance with applicable policies and laws
- Deployment and user onboarding
- Provide straightforward installation guides and troubleshooting tips
- Offer training on safe usage, phishing awareness, and device hygiene
- Establish a support channel for VPN access issues
- Ongoing governance
- Schedule regular policy reviews and audits
- Keep software and signatures updated
- Continuously monitor for new vulnerabilities and adjust controls accordingly
Common threats and how to mitigate them
- Credential theft: Use MFA, enforce device posture, and monitor for unusual login locations
- Endpoint compromise: Enforce device health checks, antivirus, and least privilege
- Misconfigured split-tunnel: Prefer full-tunnel for sensitive data; if split-tunnel is used, enforce strict routing policies
- Data leakage on endpoints: Implement data loss prevention DLP policies and restricted copy-paste rules
- Network eavesdropping on untrusted networks: Ensure VPN encryption is robust and verified through tests
- Third-party vendor risk: Conduct vendor risk assessments and require security attestations
Best practices for ongoing safety and compliance
- Regularly update and patch VPN software and endpoints
- Conduct annual or semi-annual security audits and third-party assessments
- Maintain clear incident response and disaster recovery plans
- Keep user education current with phishing and social engineering awareness
- Document all configurations, changes, and access policies for audits
VPN safety in different environments
- Remote federal employees: Prioritize MFA, device posture checks, and full-tunnel VPN with strict access controls
- Contractors and temporary staff: Use time-bound access, RBAC, and automated revocation when contracts end
- Mobile devices: Enforce secure config, app whitelisting, and platform security features
- Public or unsecured networks: Always use VPN with strong encryption and verify server certificates
Data privacy considerations Nordvpn e wireguard la guida definitiva per sfruttare la massima velocita e sicurezza
- Understand what data is logged and who can access it
- Prefer vendors with transparent privacy policies and independent audits
- Ensure data transfer and storage comply with applicable laws and government regulations
- Separate personal and work traffic where possible to reduce privacy concerns
Deployment case studies and lessons learned
- Case study A: A government agency migrated from a legacy VPN to a modern, MFA-enabled solution. Result: reduced breach incidents and improved incident response times.
- Case study B: A federal contractor implemented device posture checks and RBAC, cutting unauthorized access by 60% within six months.
- Case study C: A university research center used a split-tunnel VPN with strict routing rules to balance performance and security, while maintaining compliance.
Table: Key VPN features to compare at-a-glance
- Feature: Encryption strength
- Description: AES-256 or stronger, secure key exchange
- Feature: Authentication
- Description: MFA, certificate-based or hardware tokens
- Feature: Access control
- Description: RBAC, least privilege, time-bound access
- Feature: Endpoint posture
- Description: Device health checks before granting access
- Feature: Logging
- Description: Audit logs, access logs, with restricted retention
- Feature: Compliance
- Description: Aligns with NIST, FISMA, DoD requirements
- Feature: Incident response
- Description: Clear procedures and notifications
Checklists to keep you on track
- Security readiness checklist:
- All users have MFA enabled
- Endpoints are encrypted and patched
- VPN uses strong encryption and updated protocols
- Access policies enforce least privilege
- Logs are retained per policy and accessible to auditors
- Deployment readiness checklist:
- VPN server hardened and patched
- User guides and onboarding material prepared
- Training completed on phishing, social engineering, and security hygiene
- Incident response plan tested and updated
- Compliance checklist:
- DoD/NIST alignment documented
- Data handling policies in place
- Audit trails enabled and secure
Troubleshooting quick tips
- Connection drops: Check server load, network conditions, and certificate validity
- MFA failures: Verify time sync, token status, and backup codes
- Slow performance: Use performance monitoring, verify routing, and consider full-tunnel with optimized paths
- Access denial: Confirm RBAC assignments, IP allowlists, and posture checks
- Certificate errors: Check certificate chain and trust store on the device
FAQ Section Ist duckduckgo ein vpn die wahrheit uber deine online privatsphare aufgedeckt
| VPN | Obfuscation | From / month | Plan | Free plan | Refund | Alipay | UnionPay | Crypto | Website opens in China | Trustpilot | |
|---|---|---|---|---|---|---|---|---|---|---|---|
 NordVPN | Turn on manually Obfuscated Servers / NordWhisper | $3.49/mo | 27 months: $94.23 | No | 30 days | ? | ✗ | ✓ | ✓ | ✗ Blocked | 4.2/5 (51,628 reviews) |
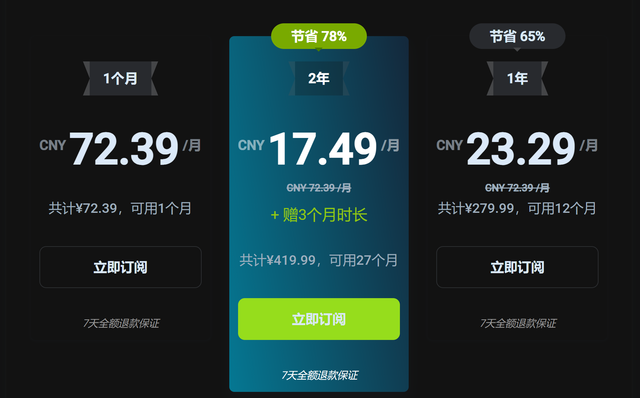
 ZoogVPN | Turn on manually Shadow | $2.49/mo | 27 months: $59.99 | Yes | 7 days | ✓ | ✓ | ✓ | ✓ | Official site blocked; our special link opens (4.4 s) | 4.2/5 (195 reviews) |
 ExpressVPN | ✓ On by default all servers | $3.00/mo | 28 months: $84 | No | 30 days | ✗ | ✗ | ✓ | ✗ | ✗ Blocked | 4.4/5 (29,706 reviews) |
 Surfshark | ✓ On by default Camouflage, with OpenVPN | See site | See site | No | 30 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.3/5 (31,823 reviews) |
 Proton VPN | Turn on manually Stealth, free plan too | $2.99/mo | 12 months: $35.88 | Yes | 30 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 2.1/5 (1,040 reviews) |
 Astrill VPN | Turn on manually StealthVPN / OpenWeb | $12.50/mo | 24 months: $300 | No | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 1.3/5 (110 reviews) |
 Private Internet Access | Turn on manually Shadowsocks, OpenVPN only | $2.03/mo | 40 months: $81.2 | No | 30 days | ✗ | ✗ | ✗ | ✗ | ✗ Blocked | 4.2/5 (11,033 reviews) |
 CyberGhost | Turn on manually selected servers | $2.19/mo | 28 months: $61.32 | No | 45 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.0/5 (24,178 reviews) |
 PureVPN | Turn on manually switch to OpenVPN | $1.69/mo | 60 months: $101.55 | No | 31 days | ? | ? | ✗ | ✓ | ✗ Blocked | 4.4/5 (17,994 reviews) |
 AdGuard VPN | ✓ On by default TrustTunnel | $2.99/mo | 24 months: $71.76 | Yes | 30 days | ✓ | ✗ | ✓ | ✓ | Official site blocked; our special link opens (3.7 s) | 4.3/5 (290 reviews) |
 Mullvad | Turn on manually QUIC / Shadowsocks / LWO | $5.61/mo | €5/mo | No | 14 days | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 3.2/5 (192 reviews) |
 Windscribe | Turn on manually Stealth / WStunnel | $5.75/mo | 12 months: $69 | Yes | See site | ✗ | ✗ | ✗ | ✓ | ✗ Blocked | 4.7/5 (13,355 reviews) |
 StrongVPN | Turn on manually Scramble, OpenVPN TCP | See site | See site | No | 30 days | ✓ | ✗ | ✗ | ✗ | ✗ Blocked | 4.4/5 (2,695 reviews) |
 LightXtreme 闪连 | Not listed | $7.08/mo | 12 months: $84.99 | Yes | 30 days | ✓ | ✓ | ✓ | ✓ | ✓ Yes (3.5 s) | No page |
Prices checked 2026-11-10 on each vendor's pricing page (cheapest long plan, USD). Check the vendor's checkout for the final price.
Obfuscation checked 2026-11-14 on each vendor's site and help center: "on by default" = nothing to set; "turn on manually" = switch protocol or mode in settings; "not listed" = the vendor describes no obfuscation.
Payment methods checked 2026-11-10 on each vendor's payment pages: all 14 take cards and PayPal; ✗ = not listed, ? = the vendor's own pages disagree.
China access: whether the official website opens from mainland China networks (tests the website only, not the VPN connection). Last checked 2026-11-18 01:02 Beijing time.
Trustpilot score and review count checked 2026-11-10.
Frequently Asked Questions
Is VPN safe for government employees using it for sensitive data?
Yes, when configured with strong encryption, MFA, device posture checks, and strict access controls, a VPN can safely protect sensitive data in government workflows.
Can split-tunneling be safe for federal use?
Split-tunneling can be risky for sensitive data. If used, it must be tightly controlled with strict routing rules, endpoint posture requirements, and comprehensive monitoring.
What encryption standards should I look for?
AES-256 or higher with modern key exchange IKEv2/IPsec or WireGuard and authenticated protocols. Avoid outdated ciphers.
How important is multi-factor authentication MFA?
Crucial. MFA dramatically reduces the risk of credential theft and is often mandatory for federal access.
Do VPNs log user activity?
Good VPNs offer configurable logging. For federal use, logs should support audits while minimizing unnecessary data retention, following policy guidelines. How to get your expressvpn refund a no nonsense guide and what to do next
Should devices be checked for health before connecting?
Yes. Device posture checks help ensure endpoints are secure before granting VPN access.
How can I verify a VPN vendor is compliant?
Look for government-facing certifications, independent third-party audits, DoD/NIST alignment, and clear data handling policies.
What is the difference between full-tunnel and split-tunnel?
Full-tunnel routes all traffic through the VPN, offering stronger security. Split-tunnel routes only some traffic through the VPN, which can improve performance but increases risk if misconfigured.
How often should VPN policies be reviewed?
At minimum annually, or after major policy changes, incidents, or new compliance requirements.
What should I do if I suspect a VPN compromise?
Activate incident response procedures, revoke compromised credentials, isolate affected devices, and perform a full forensic review. Surfshark vpn bypass not working heres how to fix it fast
If you’re ready to explore a VPN solution that fits federal use, consider checking out a well-supported option with strong security features and clear compliance posture. For more information and options, you can explore the following resource and vendor perspectives: NordVPN affiliate link - https://go.nordvpn.net/aff_c?offer_id=15&aff_id=132441